AI Code Reviewer — Enterprise Git Intelligence Platform
Built with Next.js 16 (App Router + Turbopack), React 19, TypeScript, PostgreSQL (Prisma), BullMQ & Redis, and Tailwind CSS v4. Features automated PR reviews via cryptographic GitHub App webhooks, native VS Code extension and zero-dependency CLI developer tools, in-dashboard multi-provider PR browsing, dual-depth engineering perspectives (Balanced vs. Maximum DSA/Big-O analysis), two-tier Redis caching, multi-tenant team quality dashboards, and fail-closed repository access control.
Overcoming production bottlenecks and scalability constraints.
Traditional static linters only flag trivial syntax formatting, while human code reviews struggle to consistently catch architectural rot, asymptotic complexity bottlenecks (O(n²) traps), OWASP security vulnerabilities, and cross-repo anti-patterns under tight delivery deadlines. Furthermore, developers suffer from fragmented workflows between local IDEs, terminal CLI tools, web dashboards, and CI/CD pipelines, compounded by security risks of persisting long-lived git tokens.
Engineered with disciplined primitives and modern runtimes.
Architected an omni-channel review ecosystem with unified Bearer and session authentication. Engineered an asynchronous BullMQ worker queue on Redis with PostgreSQL idempotency guarantees, two-tier commit SHA caching (Tier-1 enqueue instant HTTP 202 cost:0, Tier-2 worker refund), a native VS Code extension with inline Problems diagnostics, a zero-dependency CLI (cr), multi-provider PR browser (GitHub, GitLab, Bitbucket), cryptographic GitHub App webhooks with Checks API status gating, and an ephemeral CI token vault (X-Git-Token with 15-minute TTL).
Decisions made for durability, zero lock-in, and throughput.
Dual-Depth Engineering Perspectives & Algorithmic DSA Analysis
Enables developers to select analysis depth: Balanced Depth (~1 min) for rapid PR architecture, security, and maintainability; Maximum Depth (~2–5 min) for advanced Data Structures & Algorithms, Big-O asymptotic complexity, and low-level performance traps.
Developer Tooling: Native VS Code Extension & Zero-Dependency CLI
Local-first developer clients powered by Bearer API keys: VS Code extension provides inline code squiggles, Problems-panel diagnostics, and quick-fixes; zero-dependency CLI (cr) provides cr review pr, offline pre-PR staged checks (cr review staged), and non-destructive pre-push git hook installation.
In-Dashboard PR Browser & Connected Repo Picker
Integrated PR browser backed by GET /api/git/:provider/repos/:owner/:repo/pulls with 60-second in-memory caching across GitHub, GitLab, and Bitbucket. Repo cards and /review/pr offer one-click review triggers with depth toggles alongside manual URL paste.
Signature-Verified GitHub App & Checks API Automation
Cryptographic HMAC webhook handler (X-Hub-Signature-256) on POST /api/webhooks/github. Automatically enqueues PR reviews on open/sync, posts sticky markdown comments, and registers GitHub Check Runs that gate merges on High/Critical severity findings.
Two-Tier Redis Caching & Ephemeral CI Token Vault
Decoupled worker queue on Redis with byte-identical reviews cached by commit SHA. Tier-1 (enqueue-time) returns instant HTTP 202 (cost: 0) without queue traversal; Tier-2 (worker-time) refunds reserved credits on cache hits. Private CI reviews use ephemeral X-Git-Token (15-min TTL), consumed once by the worker and never written to disk or database.
Fail-Closed Repository Access Control & Enterprise Hardening
Enforces SELECTED_ONLY vs ALL_REPOSITORIES repo allow-lists with fail-closed denial on database downtime. Enforces strict 2MB raw webhook limits (HTTP 413 anti-DoS), SSRF file path restrictions with origin allowlists, PostgreSQL partial unique index concurrency locks, and HMAC API key peppers (API_KEY_PEPPER).
Teams, Multi-Tenancy & 90-Day Quality Dashboards
Zero data leakage ensures personal reviews never appear on team boards. Features RBAC (owner, admin, member), 7-day expiring email invites, weekly ISO quality trend charts, and team-scoped API keys with automated review stamping.
Architecture & request flows.
Asynchronous BullMQ worker queue on Redis with PostgreSQL idempotency guarantees, two-tier commit SHA caching, and GitHub Checks API gating.
[ Web Dashboard | VS Code Extension | Developer CLI (cr) | CI/CD Action | GitHub App Webhook ]
                                          │
                                          ▼
                [ Next.js 16 App Router (Turbopack) ] ── (Edge Middleware: Auth / Route Guards)
                                          │
                                          ├─► [ lib/server/requestAuth.ts ] ── (Session Cookie OR Bearer cr_live_...)
                                          ├─► [ lib/server/repoAccess.ts ] ─── (Fail-Closed SELECTED_ONLY vs ALL)
                                          ├─► [ lib/server/reviews.ts ] ────── (Idempotency & Concurrency Check)
                                          │         │
                                          │         ├─► [ Redis Cache ] (Tier-1 Enqueue Cache Hit ──► Fast 202 cost:0)
                                          │         ├─► [ Ephemeral Vault ] (X-Git-Token 15-min TTL Cache Stash)
                                          │         └─► [ PostgreSQL / Prisma ] (Reserve Credits & Create Job)
                                          │                   │
                                          │                   ▼
                                          └─► [ BullMQ Queue (Redis) ]
                                                      │
                                                      ▼
                                          [ Worker Process (scripts/worker.ts) ]
                                                      │
                                                      ├─► Token Precedence: CI X-Git-Token ──► GitHub App ──► User OAuth
                                                      ├─► Git Provider API (GitHub / GitLab / Bitbucket)
                                                      ├─► AI Review Pipeline (LLM AST Analysis & Complexity Audit)
                                                      ├─► Tier-2 Redis Cache (Default branch SHA hit ──► Credit Refund)
                                                      ├─► GitHub Checks API & Sticky Comments (Fail on High/Critical)
└─► PostgreSQL (Save Report & summaryScore Index)Dual-depth engineering perspectives.
| Perspective | Speed Benchmark | Core Focus | Recommended Use Cases |
|---|---|---|---|
| Balanced Depth (Default) | ~1 minute | Architecture, security vulnerabilities (OWASP), maintainability, test coverage, and modern best practices. | Daily PR reviews, CI check runs, continuous iterations. |
| Maximum Depth | ~2–5 minutes | Advanced Data Structures & Algorithms (DSA), Big-O asymptotic complexity, low-level performance traps, and system design flaws. | Pre-release security audits, legacy codebase refactors, mission-critical infrastructure. |
Multi-client developer surfaces.
Native VS Code Extension
Review Current PR directly from your editor. Publishes findings to the Problems panel with inline squiggles, severity badges, and automated quick-fix diff suggestions.
Zero-Dependency Developer CLI
Instant terminal workflow via cr with zero runtime dependencies. Streams review progress in real-time, displays health scores, and gates CI merges.
cr review pr --fail-on-criticalcr review staged (offline diff gate)cr install-hook (Husky / pre-push)In-Dashboard PR Browser
Multi-host PR browser scanning open PRs across GitHub, GitLab, and Bitbucket with draft badges, source → target branches, and 1-click depth review triggers.
Token precedence & fail-closed access control.
- Ephemeral CI Token (X-Git-Token): Passed via CI secrets (e.g. GitHub Actions), stashed in 15-minute TTL cache, consumed once by the worker, and never written to disk or database.
- GitHub App Installation Token: Owner-scoped token utilized for automated PR comments and Checks API gating.
- User OAuth Token: Refreshed on every git-provider sign-in, stored in the Account table, with raw tokens never sent to the browser.
- •Fail-Closed Repository Access: Defaults to
SELECTED_ONLYallow-lists. Any DB downtime or delegate failure results in automatic 403 access denial. - •Anti-DoS Webhook Limits: Enforces strict 2MB raw payload ceiling (HTTP 413) and responds with HTTP 200 post-HMAC to prevent retry storms.
- •SSRF & Path Restriction: LLM schema restricted to relative repository paths with strict origin allowlists on raw downloads.
Production interfaces & workflow engine.
Direct high-resolution captures across automated PR reviews, multi-tenant quality dashboards, BullMQ worker queues, and security hardening controls.
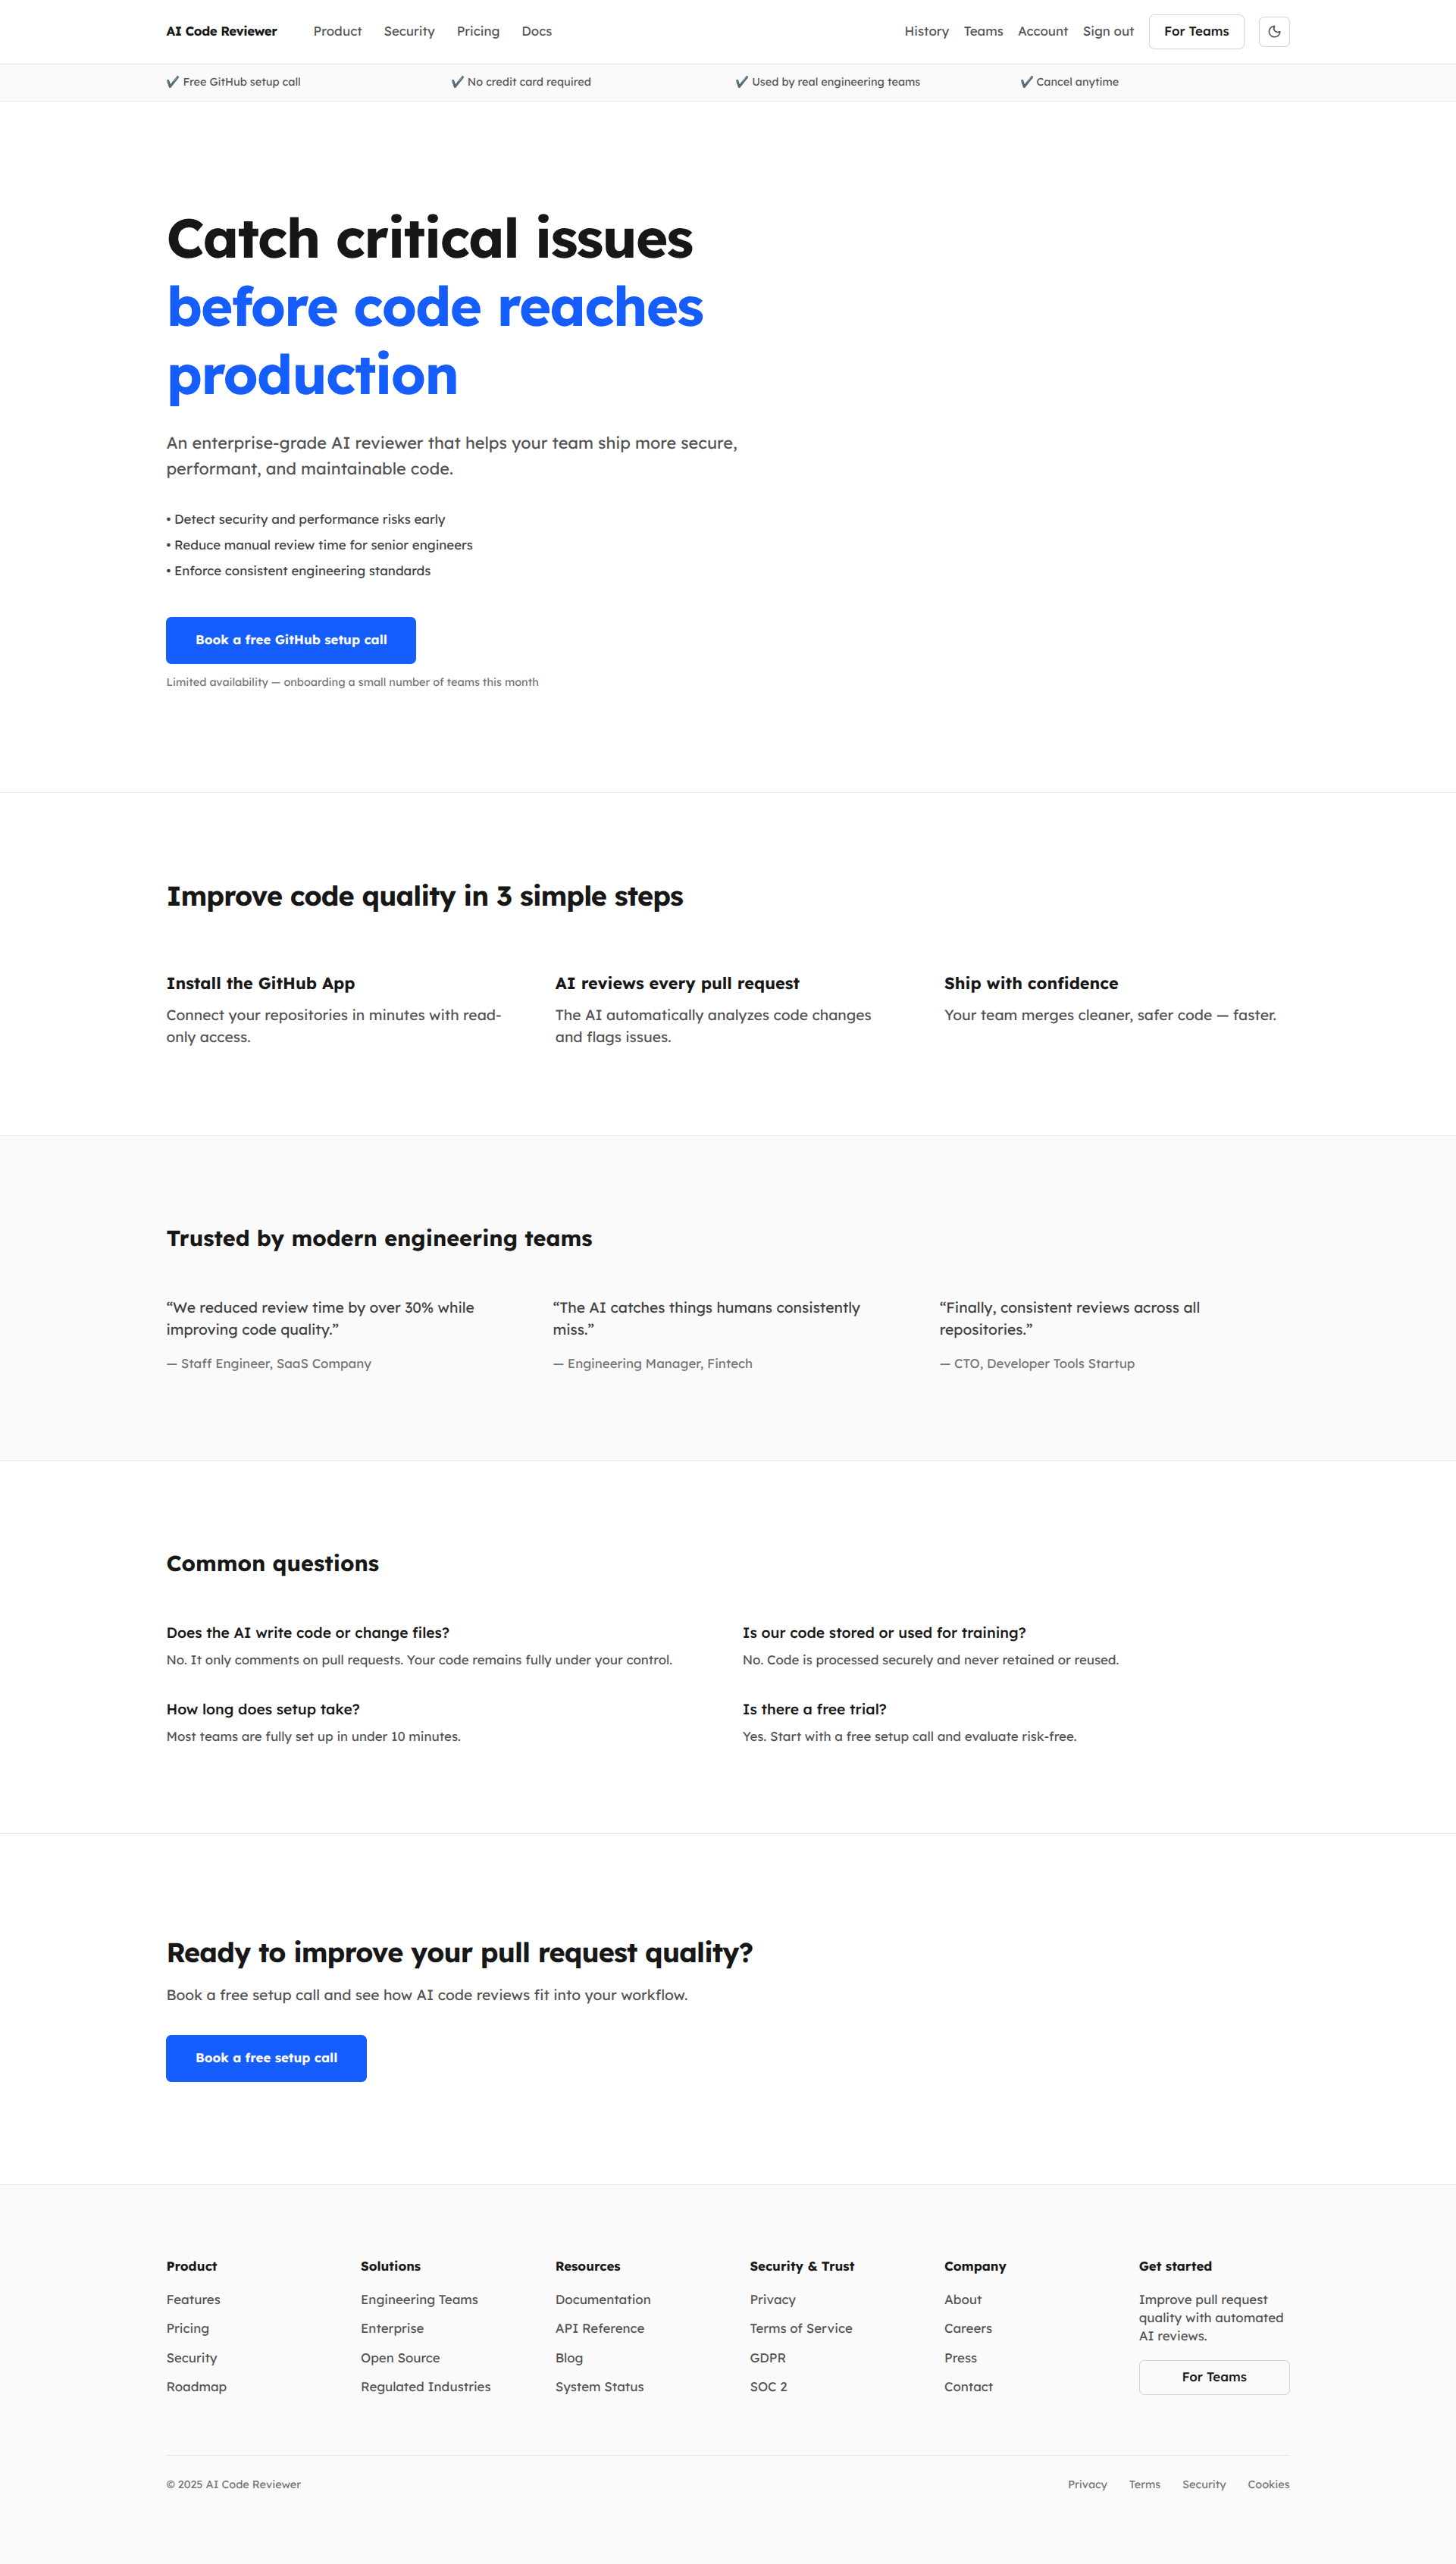
Landing page & Product Overview
Landing page with product overview, feature highlights, and call-to-action for enterprise Git intelligence platform.
Measured by results.
Processes asynchronous multi-file pull request reviews in under 45 seconds with zero timeouts, automated GitHub Checks API gating, two-tier commit caching, native VS Code & CLI integration, and seamless multi-provider Git support.