MERN Authentication & Session Engine (JWT)
A clean, production-hardened authentication boilerplate built with MongoDB, Express.js, React.js, and Node.js. Demonstrates enterprise-grade session lifecycle management using 256-bit JSON Web Tokens, bcrypt salting, protected client-side routes, and graceful error boundary handling. Has earned 83+ GitHub stars as an educational and production-grade security reference.
Overcoming production bottlenecks and scalability constraints.
Many authentication tutorials and starter kits rely on insecure token storage, unvalidated payloads, unhandled token expirations, and lack clear separation between presentation and cryptographic layers.
Engineered with disciplined primitives and modern runtimes.
Engineered a clean separation of concerns: Express middleware verifies and decodes 256-bit signed JWTs, bcrypt salts credentials with 10 rounds, MongoDB stores user models with unique email indexes, and React client context exposes declarative useAuth hooks for route protection.
Decisions made for durability, zero lock-in, and throughput.
Cryptographic JWT Session Lifecycle
Stateless JSON Web Token generation with configurable expiration, tamper-proof signature verification, and secure payload transport.
Bcrypt 10-Round Password Salting
Adaptive cryptographic hashing preventing rainbow table attacks and credential leaks with automatic salt generation.
Protected Route Guards & Context
Declarative React Router route wrapping ensuring unauthorized requests are intercepted before sensitive UI components render.
Resilient Error Handling & Toast Feedback
Unified backend error middleware and client-side notifications preventing sensitive credential leakage while giving clear user feedback.
Production interfaces & workflow engine.
Direct high-resolution captures across automated PR reviews, multi-tenant quality dashboards, BullMQ worker queues, and security hardening controls.
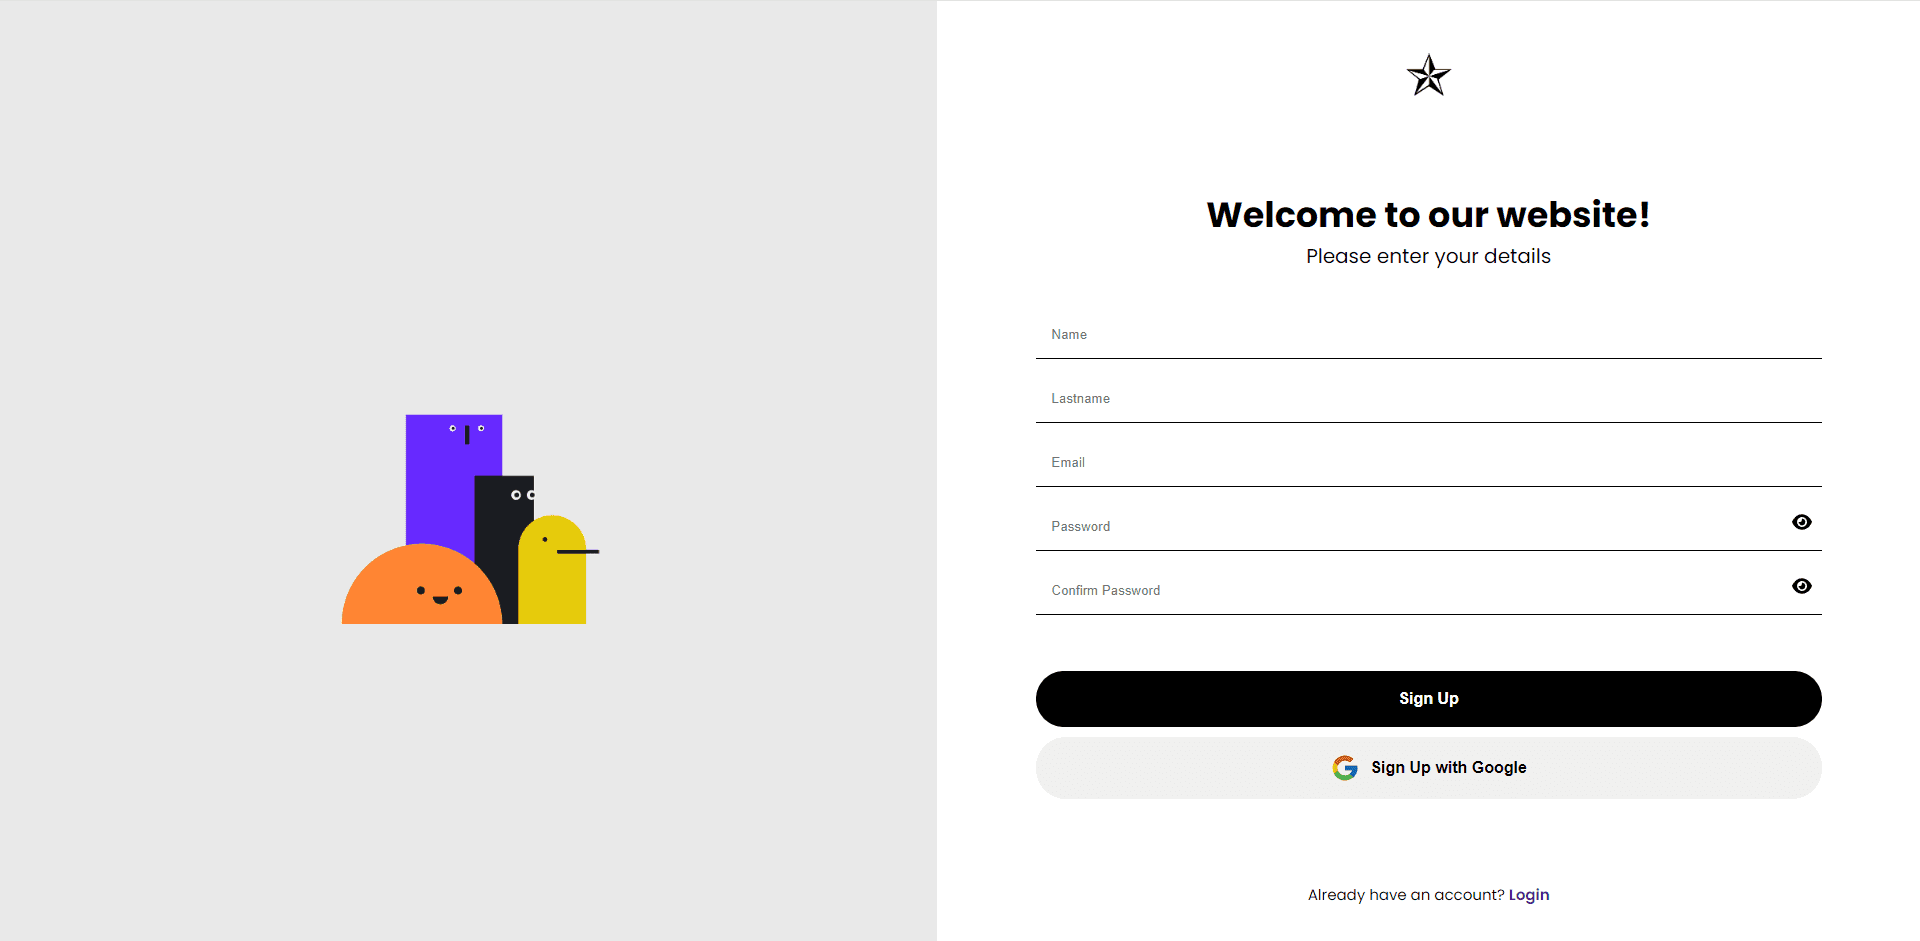
MERN User Registration & Credential Hashing
User account creation flow validating email format, password complexity, and executing bcrypt hashing.
Measured by results.
Earned 83+ GitHub stars as an educational and production-ready reference for developers mastering full-stack user authentication and session security.
Empirical Verification Framework
Unsafe plain-text or poorly salted credentials with unhandled client session expirations
256-bit signed JWTs, 10-round bcrypt hashing, and instant client route gating
Postman API security test collections & OWASP authentication verification checklist (2024 continuous release)
Express.js backend with MongoDB Atlas cluster and Vite React client — Demonstration environment uses Bearer tokens; production enterprise deployments can pair with HTTP-only cookies.